Why ISO 27001 Matters When You Outsource AML Compliance (and Why So Few Firms Have It)
Your compliance provider sees your most sensitive data. ISO/IEC 27001 proves they protect it, and very few firms in Canada are certified. AML Incubator is one of them.
ISO/IEC 27001 is the international standard for keeping information safe. A company that is certified has passed an independent audit showing it protects sensitive data with proper controls, risk checks and ongoing reviews. It matters most when you outsource AML compliance, because your provider handles your customers' IDs, transaction data and suspicious transaction reports.
AML Incubator is ISO/IEC 27001:2022 certified.
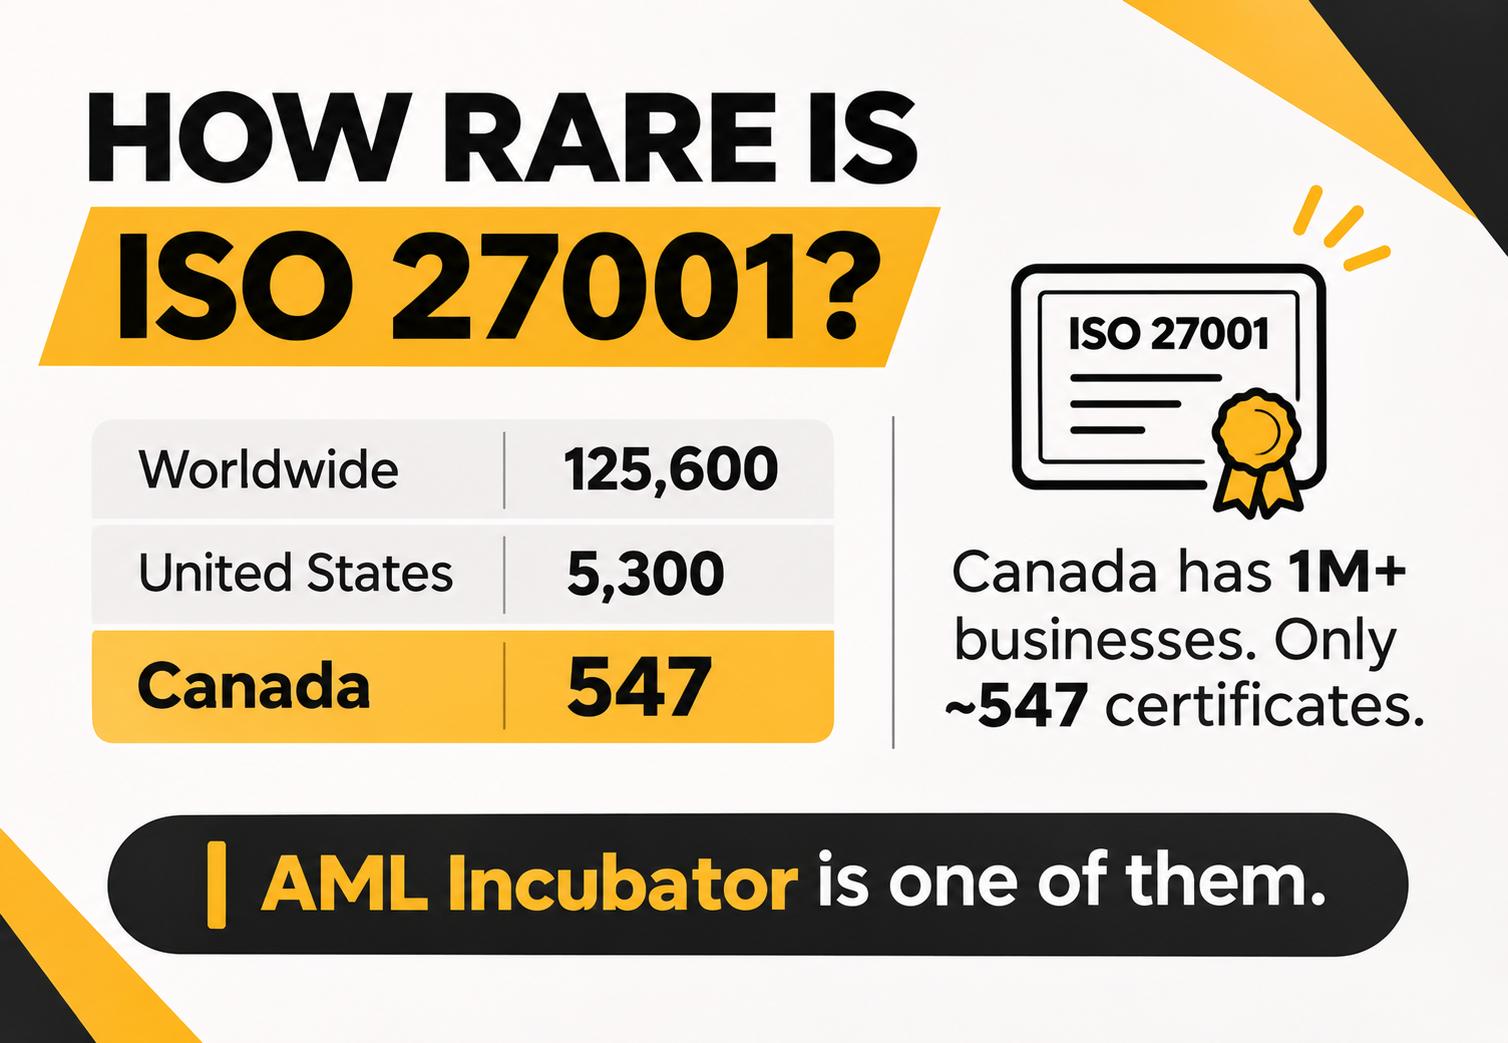
Only about 547 organizations in all of Canada held the certificate at the end of 2025.
What is ISO 27001?
ISO/IEC 27001 is a global standard published by ISO (the International Organization for Standardization). It sets out how a company should run an information security management system: the rules, controls and habits that keep data safe.
To get certified, a company has to:
- Find its risks: work out what could go wrong with the data it holds, from hacking to human error
- Put controls in place: access rules, encryption, secure offices, staff training, supplier checks and more
- Pass an independent audit: an accredited certification body checks that everything actually works, not just on paper
- Keep it up: surveillance audits every year, and a full recertification every three years
The 2022 version is the latest.
It added newer controls such as threat intelligence, cloud security and data leakage prevention.
Why so few companies have it
ISO 27001 takes months of work, real investment and outside audits that keep going every year. Most companies never do it.
| ISO 27001 certificates (end of 2025) | |
|---|---|
| Worldwide | about 125,600 |
| United States | about 5,300 |
| Canada | about 547 |
Canada has more than a million businesses. Only a few hundred hold an accredited ISO 27001 certificate.
AML Incubator is one of them.
Why it matters when you outsource AML compliance
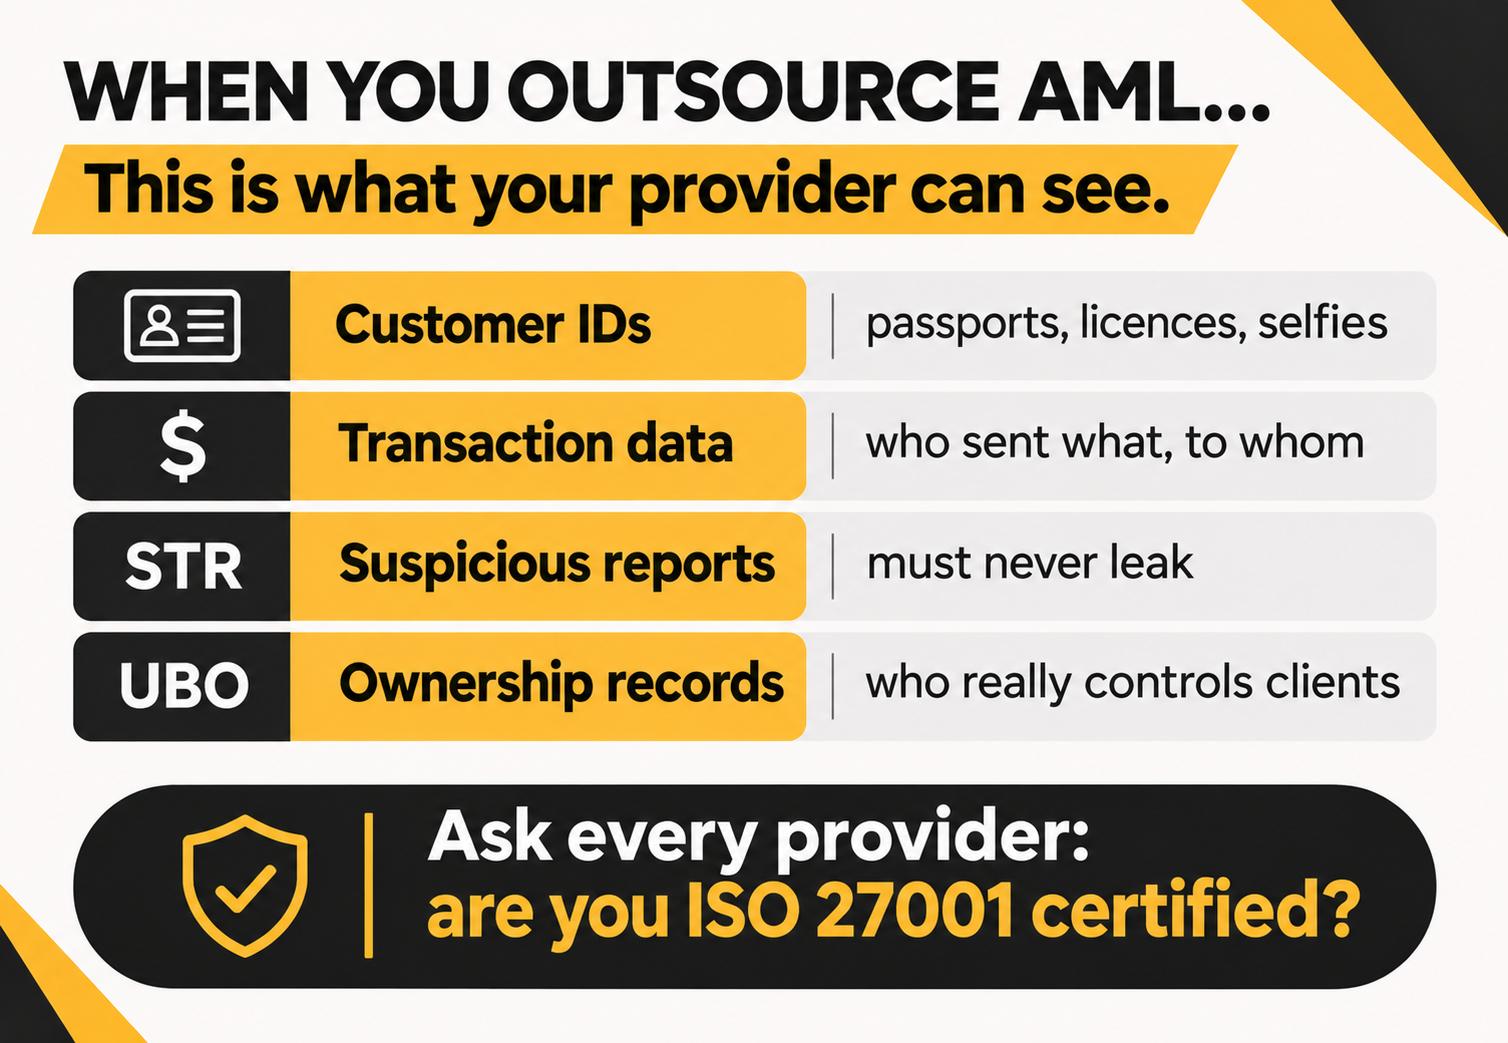
When you hire a compliance firm, a CAMLO or an outsourced KYC team, you're handing over some of the most sensitive data your business has:
- Customer IDs and KYC files: passports, driver's licences, proof of address, selfies
- Transaction data: who sent what, to whom, and when
- Suspicious transaction reports (STRs): confidential reports to FINTRAC that must never leak to the customer
- Beneficial ownership records: who really owns and controls your clients
- Your own policies, risk assessments and exam findings
If that data leaks, it isn't only your provider's problem. It's yours. You stay responsible for your compliance program and your customers' privacy, even when someone else runs it.
That's why more banks, payment partners and investors now ask fintechs and MSBs one simple question: "Who has access to your compliance data, and how do you know it's safe?"
What an ISO 27001 certified compliance partner gives you
- Proof: an independent auditor has checked the controls, so you don't have to take anyone's word for it.
- Easier bank and partner due diligence: banks and payment partners run vendor risk reviews. A certificate answers many of their security questions in one go.
- Better protection for your customers: this helps you meet privacy duties under Canadian law, including PIPEDA's requirement to protect personal information.
- Lower risk of tipping off: STRs and investigations stay locked down, so they can't reach the people being reported.
- A partner that keeps improving: yearly audits mean security doesn't stop after the certificate is issued.
How AML Incubator protects your data
AML Incubator Ltd. holds an active ISO/IEC 27001:2022 certificate:
| Standard | ISO/IEC 27001:2022, Information Security Management Systems |
| Certificate number | IC-IS-2605310 |
| Certification body | Intercert Inc. |
| Accredited by | Standards Council of Canada (SCC) |
| Status | Active |
| Scope | Our information security management system for Human Resources, Information Technology and Admin, with all activities carried out remotely |
What that means for you:
- Our IT systems are independently audited. These are the systems your files live on.
- Our people processes are covered. That includes hiring, onboarding, training and offboarding, so access is controlled from day one to the last day.
- Our admin and remote-work setup is covered. As a fully remote team, the security of how and where we work is part of the audit.
- Accredited, not self-declared. The certificate comes from an accredited body under the Standards Council of Canada, Canada's national accreditation body.
You can verify our certificate yourself on IAF CertSearch, the global database of accredited certificates.
5 questions to ask any compliance provider
Before you share a single customer file, ask:
- Are you ISO 27001 certified? Ask for the certificate and check it on IAF CertSearch.
- Who will see my data? Names and roles, not "our team".
- Where is my data stored? Which country, which systems, and who hosts them?
- How do you handle STRs and investigations? Who can access them, and how are they kept confidential?
- What happens if there's a breach? How fast will they tell you, and what's the plan?
If a provider can't answer these clearly, that's a red flag.
Compliance is about trust.
Regulators trust you to protect the financial system, your customers trust you with their data, and you trust your compliance partner with both.
ISO 27001 is how that trust gets proven.
Very few firms in Canada have it. AML Incubator does.
Looking for a compliance partner you can show your bank with confidence?
Book a call with AML Incubator, or see our fractional CAMLO/MLRO services.
FAQs
What does ISO 27001 certified mean?
An accredited, independent auditor has checked that the company runs an information security management system that meets the ISO/IEC 27001 standard.
Is ISO 27001 required for AML compliance firms?
No law requires it. But it's one of the strongest ways a compliance provider can prove it protects your data, and banks and partners increasingly ask for it.
How many companies in Canada are ISO 27001 certified?
About 547 certificates at the end of 2025, according to the ISO Survey.
What's the difference between ISO 27001 and SOC 2?
ISO 27001 is an international certification of a company's whole security management system. SOC 2 is a US-style audit report on specific controls. Both are useful, and ISO 27001 is more widely recognized around the world.
How long does ISO 27001 certification last?
Three years, with surveillance audits every year in between.
How can I check if a company is really ISO 27001 certified?
Search for it on IAF CertSearch, or ask for the certificate and confirm the certification body is accredited.